Policy-driven01
A policy for each path and destination
Define which field is transformed, for which consumer and by which method.
PII / API / DestinationDefined policy
 SHABDIZ
Data protection and privacy
Shabdiz controls sensitive information visibility in APIs, databases and datasets according to organizational policy, keeping data usable for testing, development, analysis and exchange.
| Field | Original data | Policy output |
|---|---|---|
| Name | Maryam Ahmadi | User 482 |
| Mobile | 09120000000 | 0912••••••• |
| Customer ID | 12004862 | 58320714 |
| Service type | Support | Support |
In this example, the numeric ID keeps its length, the name is pseudonymized and the mobile number is masked.
A closer look
Behind the name Shabdiz
World-ranging, moving at the speed of thoughtAware as the night, awake as the dawn
Nezami, Khosrow and Shirin, section 18
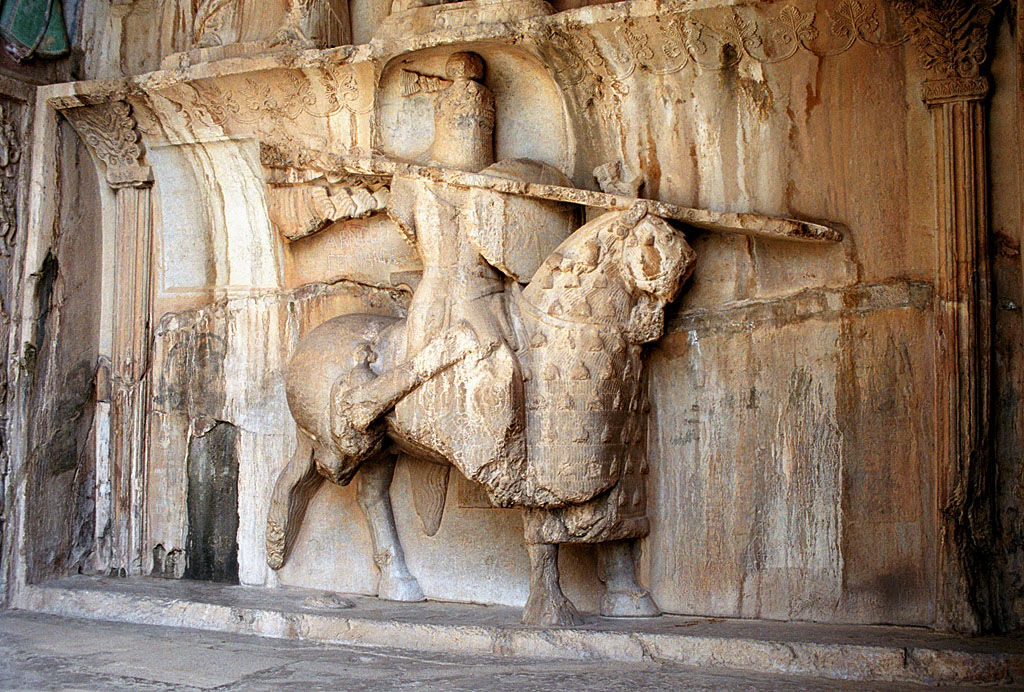
Shabdiz, the night-dark horse from the tale of Khosrow and Shirin, is known in Nezami’s poetry for its swiftness and alertness—a horse that traverses difficult paths and whose movement the poet likens to the speed of thought. Shabdiz symbolizes motion with vigilance.
For us, the name Shabdiz recalls this pairing: data must keep flowing, serve development and analysis, and lay the groundwork for better decisions; yet not every destination needs to see every identity. The value of data lies in its use, and trust and vigilance in protecting what must not be revealed.
The Shabdiz system turns this perspective into a protection policy: sensitive information is anonymized or made fictitious during exchange or dataset preparation, according to the consumer’s needs. An appropriate method and output validation help the data remain usable with the same appearance and structure as the original data, while keeping identity disclosure under control.
Data continues on its way; identity travels with it only as needed.01At a glance
A layer between data owners and consumers to control what becomes visible.
Shabdiz processes sensitive fields through masking, pseudonymization, hashing and format-aware transformations. Protection methods are selected according to use and destination.
For test data, API exchange, contractor collaboration or data preparation for analytics and AI, especially when technical access alone should not permit viewing every detail.
Banking and insurance, operators, public services, healthcare and data-driven businesses: wherever customer, citizen, employee or partner information moves between teams and systems.
Security and data leaders, enterprise architects, database, development, API, testing, analytics and AI teams.
02Key capabilities
Method selection starts with consumer needs: what must remain visible, what must change and which relationships must be preserved?
Define which field is transformed, for which consumer and by which method.
Control sensitive data visibility according to consumer needs.
Replace direct identifiers with pseudonyms in operational or analytical scenarios.
When recovery is unnecessary, design a hashing method appropriate to the data type.
Suitable transformations account for the length, type and pattern required by the destination system.
Within a consistent scope and policy, repeated identifiers receive the same substitute to preserve record relationships.
Examples illustrate the methods; operational policies depend on data types and destination-system requirements.
03Two use areas
Flow and Vault are two uses of one product. Choose an area to see its data path, inputs and outputs.
Data in Motion
When data moves between APIs, services or organizational systems, protection policies apply during exchange so consumers receive only the information they need.
Data at Rest
When development, testing or analysis needs data, define the sources and columns, then process them using suitable policies to prepare a usable copy for the destination environment.
Protection with usability
Protecting data while destroying the required structure also stops testing or analysis. Shabdiz chooses transformations with regard to data type, length and pattern.
With consistent transformations and compatible policies, relationships between records can also be preserved so the destination team can continue working with the data.
Conceptual illustration with a synthetic identifier
04Use scenarios
QA teams need data with a usable structure.
A transformed copy for development, testing and UAT.
API consumers do not need all personal information.
A protected response based on that path’s policy.
Support and collaboration require data, while identity visibility must remain limited.
A payload or dataset suited to the other party’s use.
Personal identifiers may enter analytics or AI workflows together with the data.
Transform sensitive fields before structured data enters the consumption pipeline.
05From policy to execution
We start by understanding the source and deliver output assessed against both organizational policies and consumer needs.
Identify sources, structure and sensitive fields.
Choose protection methods based on data, use and destination.
Apply policies in the API path or dataset processing.
Check format, output quality and consumer functionality.
Log operations and update policies as requirements change.
06Integration and deployment
Shabdiz works independently of other Faraconesh products. Starting with one API path or dataset enables output evaluation and gradual expansion.
Deploy in organizational infrastructure or a private environment, aligned to confidentiality requirements, service architecture and access controls.
Development and deployment experience exists on MySQL and Oracle; versions, data types and connection methods are determined in the technical review.
Depending on the scenario, Shabdiz can provide data protection alongside other products.
Before you start
Choose protection methods by understanding the data and consumer needs.
No. Shabdiz has no editions. Flow and Vault are two uses of one product: protecting data in transit and stored data. A project may cover either or both.
Start with your challenge
Let’s identify your data sources, consumption path and protection needs, then explore the right Shabdiz scope together.